Blog
Tutorials, guides, and insights to help you become a better developer.
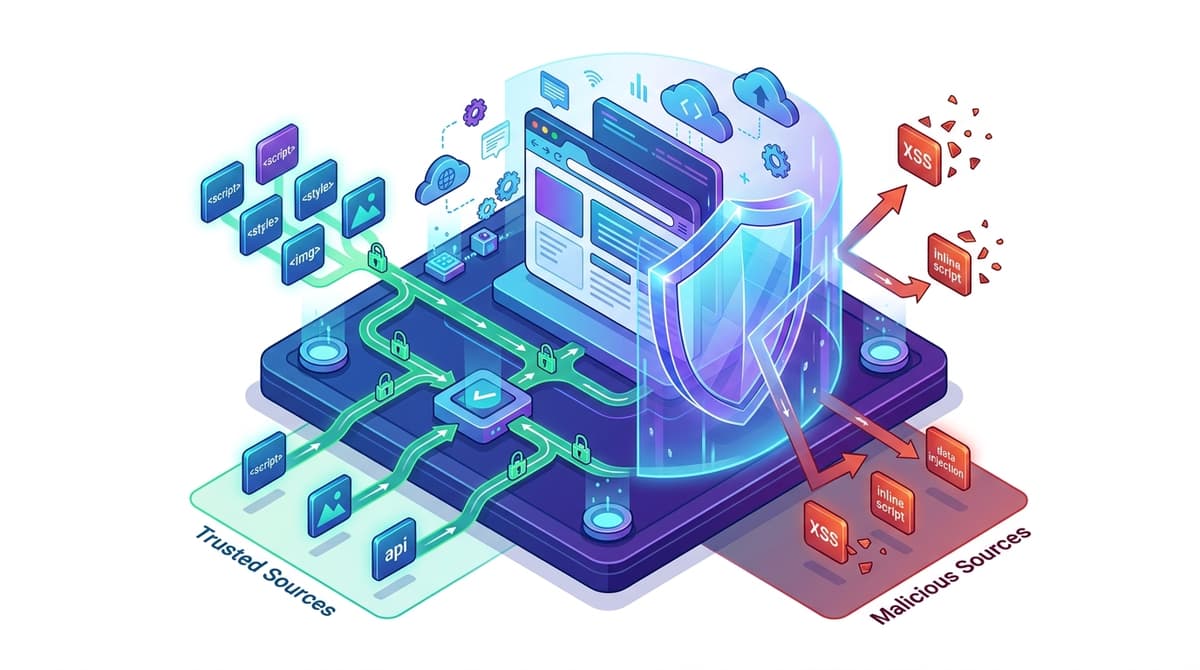
The British Airways skimmer sat in a first-party file, so no host allowlist, no 'self' and no nonce would have stopped it — here is one CSP header tightened four times, broken after each round against the CSP Level 3 matching algorithms, until only the directive nobody writes first is left holding.
AdminAugust 11, 202612 min read
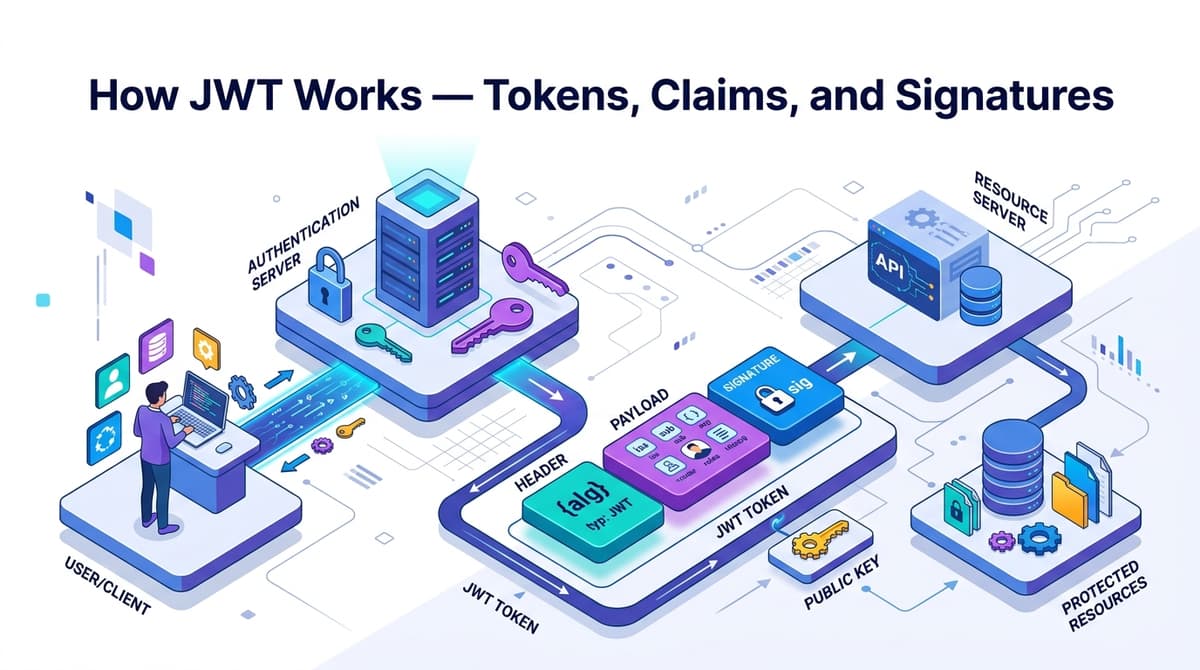
Take a JSON Web Token apart segment by segment, build a signer and verifier with nothing but node:crypto, then run the alg:none and RS256-to-HS256 key-confusion attacks against both your own code and jose@6.2.8 to see exactly which one still forges an admin token.
AdminAugust 6, 202611 min read
Client-side validation is UX. Server-side validation is security. And a schema is not an auth guard — here's the fix that still ships an account takeover, and how to catch it in review.
AdminAugust 5, 20269 min read
TLS isn't just a padlock — it's a carefully choreographed cryptographic handshake. Here's what actually happens between your browser and the server, with the openssl commands to see each step yourself.
AdminMarch 6, 202611 min read