Blog
Tutorials, guides, and insights to help you become a better developer.
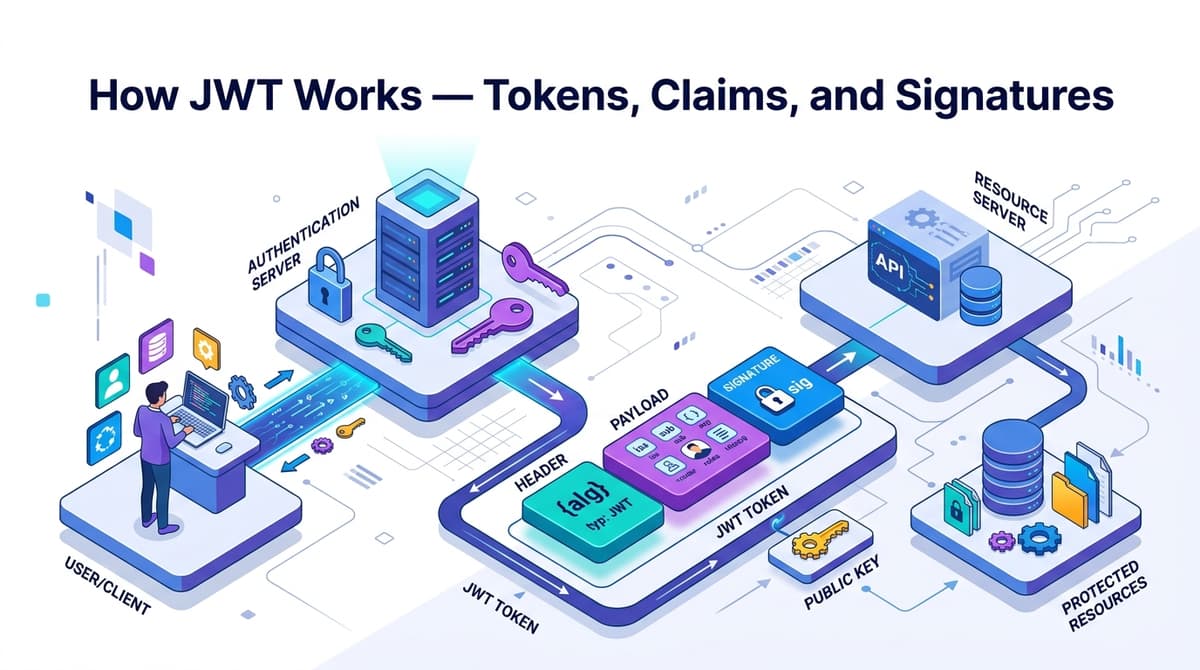
Take a JSON Web Token apart segment by segment, build a signer and verifier with nothing but node:crypto, then run the alg:none and RS256-to-HS256 key-confusion attacks against both your own code and jose@6.2.8 to see exactly which one still forges an admin token.
AdminAugust 6, 202611 min read
One file to guard every route — plus the Next.js 16 rename that moves it off the Edge runtime, the request-vs-response header trap that leaks user IDs to the browser, and the CVE that explains why this can never be your only auth layer.
AdminAugust 3, 20268 min read